 how-to
How to Verify Browser-Based File Privacy
Last Updated: October 22, 2026
Quick Summary
Browser-based file privacy verification means using your browser's Network tab to confirm files stay on your device rather than uploading to servers. Check the Network log for POST requests containing your file contents, inspect browser storage for persistent file data, test offline functionality, and compare the tool's privacy policy claims against what you observe.
- Use the Network tab with a uniquely tagged test file to search for file-bearing requests that indicate server uploads.
- Local processing tools show no POST requests with file data in their payload and typically work offline after loading.
- Inspect Application storage areas like IndexedDB and Cache Storage before and after file operations to detect persistent data.
- Read privacy policies for explicit local-processing language and cross-check claims against your Network log findings.
- Client-side verification cannot guarantee server practices, code integrity, or what happens after you close the browser.
Table of Contents
- Why Verifying Browser-Based File Privacy Matters
- Understanding Client-Side File Processing
- Using Browser Developer Tools Network Tab to Inspect File Transfers
- How to Tell If a Website Uploads Files to Its Servers
- Testing Browser Fingerprinting and Tracking
- Creating an Online File Privacy Checklist
- Limits of Client-Side Verification and What You Cannot Test
- Frequently Asked Questions
Why Verifying Browser-Based File Privacy Matters
When you upload a file to a web application, you're trusting that the tool processes it privately. But how do you actually verify that claim?
That's where browser-based file privacy verification becomes essential: you need concrete proof files stay on your device.
This guide walks you through the exact steps to test whether a web-based file tool actually keeps your data local.
Understanding Client-Side File Processing
Client-side file processing means your browser handles the work, not a remote server. Your data stays within your browser's memory and storage.
Server-side tools upload your file, process it remotely, and send back the result, creating risks: network transmission, server storage, third-party access, and loss of control. Client-side processing eliminates all of these.
Using Browser Developer Tools Network Tab to Inspect File Transfers
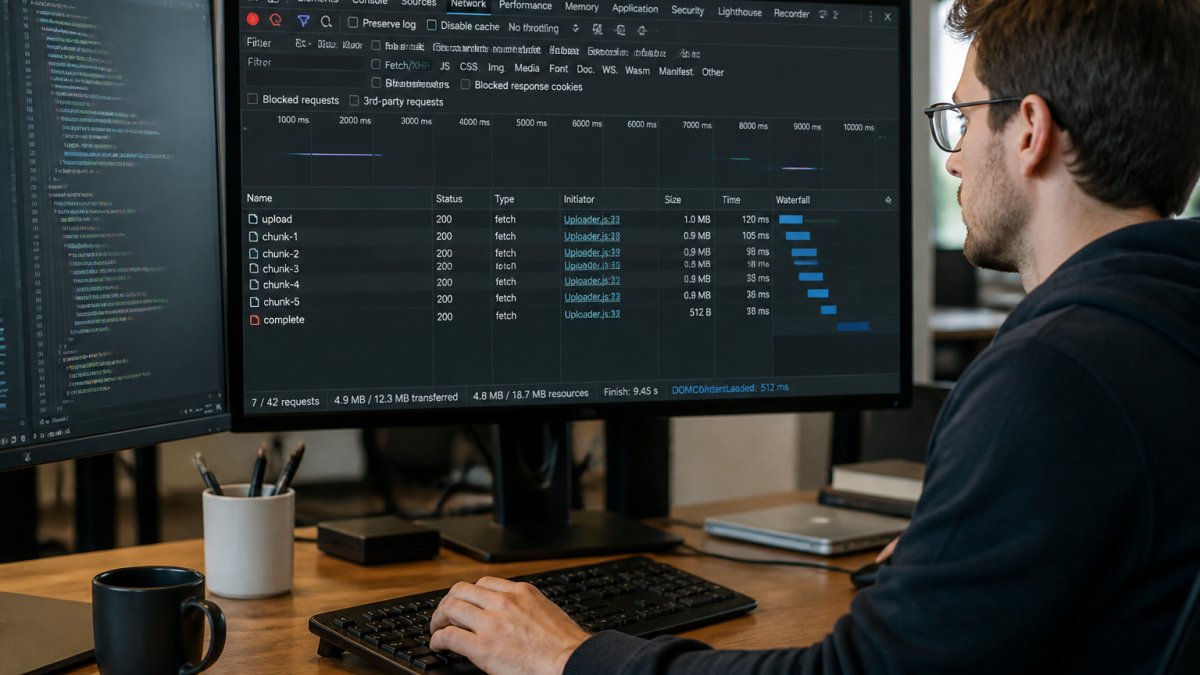
The Network tab in browser developer tools is your primary verification tool. It records every request your browser makes, including any carrying file bytes off your device, a reproducible record you can compare before, during, and after a file operation.
Set Up a Clean, Repeatable Test
Before you touch the tool you are testing:
- Use a fresh browser profile or a private window. Extensions can inject their own requests and muddy the picture; if you must test with extensions enabled, note which are active.
- Create a harmless, uniquely identifiable test file. Put a unique string inside a plain-text file, a random phrase plus today's date, and give it a distinctive name like
privacy-probe-2026-10-22.txt. If that string appears in a request payload, you have proof the file contents left the browser. - Disable cache and preserve the log. Check "Disable cache" and enable "Preserve log" so requests survive page navigations and reloads.
- Clear the log, then perform one action. One action per recording keeps attribution clean.
Open Developer Tools and Start Recording
Open developer tools with F12 (Windows/Linux) or Command+Option+I (Mac), select the Network tab, and confirm the record button is red. Reload once with recording on to capture baseline requests before any file is involved.
Filter and Read the Request List
Use the filter bar to narrow the noisy list:
- Type
method:POSTto show only POST requests, the method most commonly used for uploads. - Try the Fetch/XHR filter to isolate requests made by the page's JavaScript rather than document loads.
- Search the filter box for your test file's unique string. If it shows up in a request, that request is carrying your file contents.
For each candidate request, inspect these panels:
- Headers, check the request URL, method, and
Content-Type. Amultipart/form-datacontent type on a POST is the classic file-upload signature, and aContent-Lengthroughly matching your file size is another strong signal. - Payload / Request Body, if you see your unique string, the file was transmitted; if you see only a filename, MIME type, or byte count, the file itself was not sent.
- Response, check whether the server returned a file, a processing result, or just an acknowledgment.
What Local Processing Looks Like in the Network Log
When a tool genuinely processes files in the browser, JavaScript bundles load up front, your upload action triggers no request whose payload contains file bytes, any requests that fire are small (telemetry, license checks), and the result appears without a large request/response pair.
When a tool uploads, you will usually see one of these patterns:
- A single
multipart/form-dataPOST whose payload contains your file or its contents. - A chunked sequence of PUT or POST requests to a storage endpoint, each carrying a slice of the file.
- A presigned-URL pattern: a small request to obtain an upload URL, followed by a PUT of the file to a storage domain.
Check for Requests That Bypass the Obvious Path
Uploads don't always look like uploads. After your test action, scan the whole log, not just POSTs, for:
- Requests to domains other than the one in the address bar (storage buckets, CDNs, analytics, error-reporting services).
sendBeaconcalls, which fire on page unload and are a common way to ship data quietly.- WebSocket frames, visible under the WS filter, which can carry file data outside the normal request/response flow.
If the only requests after your upload are small and contain no file bytes, that is meaningful evidence of local processing, but see the limits section for what it does and does not prove.
Record Your Evidence
Right-click the request list and choose Save all as HAR with content, a JSON log of every request, response, header, and timing. Keep it with your notes: test file name, unique string, timestamp, and browser version. For a team evaluation, a HAR plus a short summary beats "I looked and it seemed fine."
How to Tell If a Website Uploads Files to Its Servers
Network inspection shows what left the browser. This section covers complementary evidence: what the tool does with your file inside the browser, what it leaves behind, and how to read a privacy policy.
Check Where the File Lives Inside the Browser
A local-processing tool still holds your file somewhere in the browser. Knowing where to look tells you whether that storage is transient or persistent.
- Object URLs and blob URLs. Local tools commonly create a
blob:URL to hand file data to an image, video, or download element. Look for blob entries in the Application (Chrome/Edge) or Storage (Firefox) panel; if a blob URL survives a reload, the underlying data may be persisted. - IndexedDB. A local-processing tool may use IndexedDB as scratch space for large files. Persistent records containing file data after you close and reopen the tool are a retention signal.
- Cache Storage and the Cache API. Service workers often cache assets and sometimes data. Inspect it for entries that appear only after a file operation.
A useful test: perform a file operation, close the tab entirely, reopen the tool, and re-inspect these storage areas. Data that persists across a full tab close is data the tool chose to keep.
Use the Offline Test Properly
Load the tool, let it finish loading, then disconnect your network (turn off Wi-Fi or use offline mode in the Network tab) and perform the file operation.
Run the test twice: once with a small file and once with a file large enough that an upload would be obvious in the Network log. A tool that works offline for small files but stalls on large ones may be uploading above a size threshold.
Treat Speed and Size Limits as Weak Signals
Speed and file-size limits are commonly cited shortcuts, but they're easy to fake. Use them as tie-breakers, not evidence:
- Speed: local processing is often near-instant, but a slow device or large file can make it slow too. Compare the same file on the same device across two tools rather than relying on absolute times.
- Size limits: generous limits are consistent with local processing, but a server-backed tool can also stream large files. A strict limit under 10 MB is a hint, not proof.
Read the Privacy Policy for the Claims That Matter
Policy language isn't verification, but it tells you what the vendor commits to. Look for:
- Explicit local-processing language. Phrases like "processed in your browser," "never leaves your device," or "client-side processing" are the claims to test against your Network log.
- Retention periods. Find the retention window and deletion mechanism; "retained for 30 days" and "deleted immediately after processing" are very different commitments.
- Deletion controls. Does the tool offer a delete button, an account-level purge, or a documented deletion request process?
Run a Repeatable Test Case
Combine the checks into one repeatable workflow:
- Create a text file containing a unique tracer string and a distinctive filename.
- Open a fresh profile, enable Preserve log and Disable cache, and record a baseline.
- Perform the file operation once and search the Network log for the tracer string.
- Inspect Application → IndexedDB, Cache Storage, and Service Workers before and after the operation.
- Close the tab, reopen the tool, and re-inspect storage for persistence.
- Repeat offline and with a large file.
- Export a HAR and note the policy's retention and third-party claims.
A tool that fails step 3 has uploaded your file, regardless of what its policy says.
Testing Browser Fingerprinting and Tracking
Browser fingerprinting is a separate privacy concern from file uploads: a tool might process your file locally but still track your behavior.
To test for fingerprinting, use a browser privacy test tool. These tools show what information websites can detect about your browser.
Check for these fingerprinting signals:
- Timezone detection
- Screen resolution tracking
- User agent analysis
If a tool collects this data but doesn't process files locally, that's a partial win. Your file stays private, but your behavior is tracked.
Creating an Online File Privacy Checklist
Use this checklist to evaluate any browser-based tool systematically.
| Test | What to Look For | Pass = | Fail = |
|---|---|---|---|
| Network tab inspection | No file uploads to servers | Zero POST requests with file data | File data in request payload |
| Processing speed | Instant or near-instant results | ||
| Offline functionality | Tool works without internet | Tool functions offline | Tool requires internet |
| Privacy policy language | Explicit local processing claims | "Processed in your browser" stated | Vague or missing language |
| Third-party requests | No tracking or analytics | Requests only to main domain | Requests to ad networks |
| File size limits | Generous limits reflecting local processing | ||
| Fingerprinting detection | No browser fingerprinting | Privacy test shows no tracking | Privacy test detects tracking |
Work through this checklist before uploading sensitive files. Each passing test increases confidence in the tool's privacy claims.
Limits of Client-Side Verification and What You Cannot Test
Client-side verification has real boundaries; understanding them prevents false confidence.
You cannot verify what happens after you close the browser.
You cannot verify server-side practices. The Network tab shows what leaves your browser, not what the server does with data it receives.
You cannot test forensic recovery. According to Purdue University's comparative forensic analysis, privacy-enhanced browsers in private-browsing mode still leave artifacts that forensic tools can examine.
You cannot verify code integrity.
These limits don't make client-side verification useless, it's one part of a complete privacy strategy.
Browser-based file privacy verification is a learnable skill that requires effort and skepticism.
Frequently Asked Questions
How can I check whether a browser-based tool uploads my files?
Open your browser's developer tools (F12 or right-click > Inspect), go to the Network tab, then upload your file. Watch for POST or PUT requests to external servers. If no requests appear and the tool processes your file without network activity, it's likely processing locally. Check the request payload to confirm no file data is being sent. HTTPS encryption alone does not guarantee local processing, you must inspect actual network traffic.
What is the difference between client-side file processing and server-side processing?
Client-side file processing means your browser handles the file entirely on your device, no data leaves your computer. Server-side processing sends your file to the website's servers for handling. Client-side is more private because the service provider never sees your file. You can verify client-side processing by checking the Network tab for file uploads; if no file data appears in outgoing requests, processing is likely happening in your browser.
Does HTTPS mean a browser-based file tool is private?
No. HTTPS encrypts data in transit between your browser and the server, but it does not guarantee that files stay on your device. A tool using HTTPS can still upload your files to its servers, the encryption just makes the transfer secure from interception. To verify true privacy, inspect the Network tab for file uploads. If encrypted HTTPS requests contain your file data, the tool is sending it to a server, even though the connection is secure.
What should I check in a privacy policy before using an online file tool?
Look for explicit statements about file retention and deletion. Ask: Does the tool delete files immediately after processing, or does it store them? Does it use your files for training AI models? Does it share files with third parties? Check whether the tool claims client-side processing and look for technical details about how it works. Cross-check policy claims against actual network activity using developer tools. A strong privacy policy combined with verified local processing offers the best assurance.